One pipeline, three surfaces.
A target moves from discovery, to a proven exploit, to an auditable report, without leaving your perimeter.
Four stages, one chain of custody.
Each stage hands the next a verified artifact, so the report at the end can be replayed from the intake that started it.
Discovery
Agents read your code, crawl your apps, and map every surface an attacker could reach. Before anyone writes a test.
Validation
The Validator reproduces each exploit against the running target and captures the evidence. If it does not run, it does not ship.
Governance
Every scan carries a complete chain of custody, mapped to the frameworks your auditors use, and gated before release.
Sovereignty
By default every model call stays inside your environment and in-country, and each outbound decision is logged.
Prove it is real.
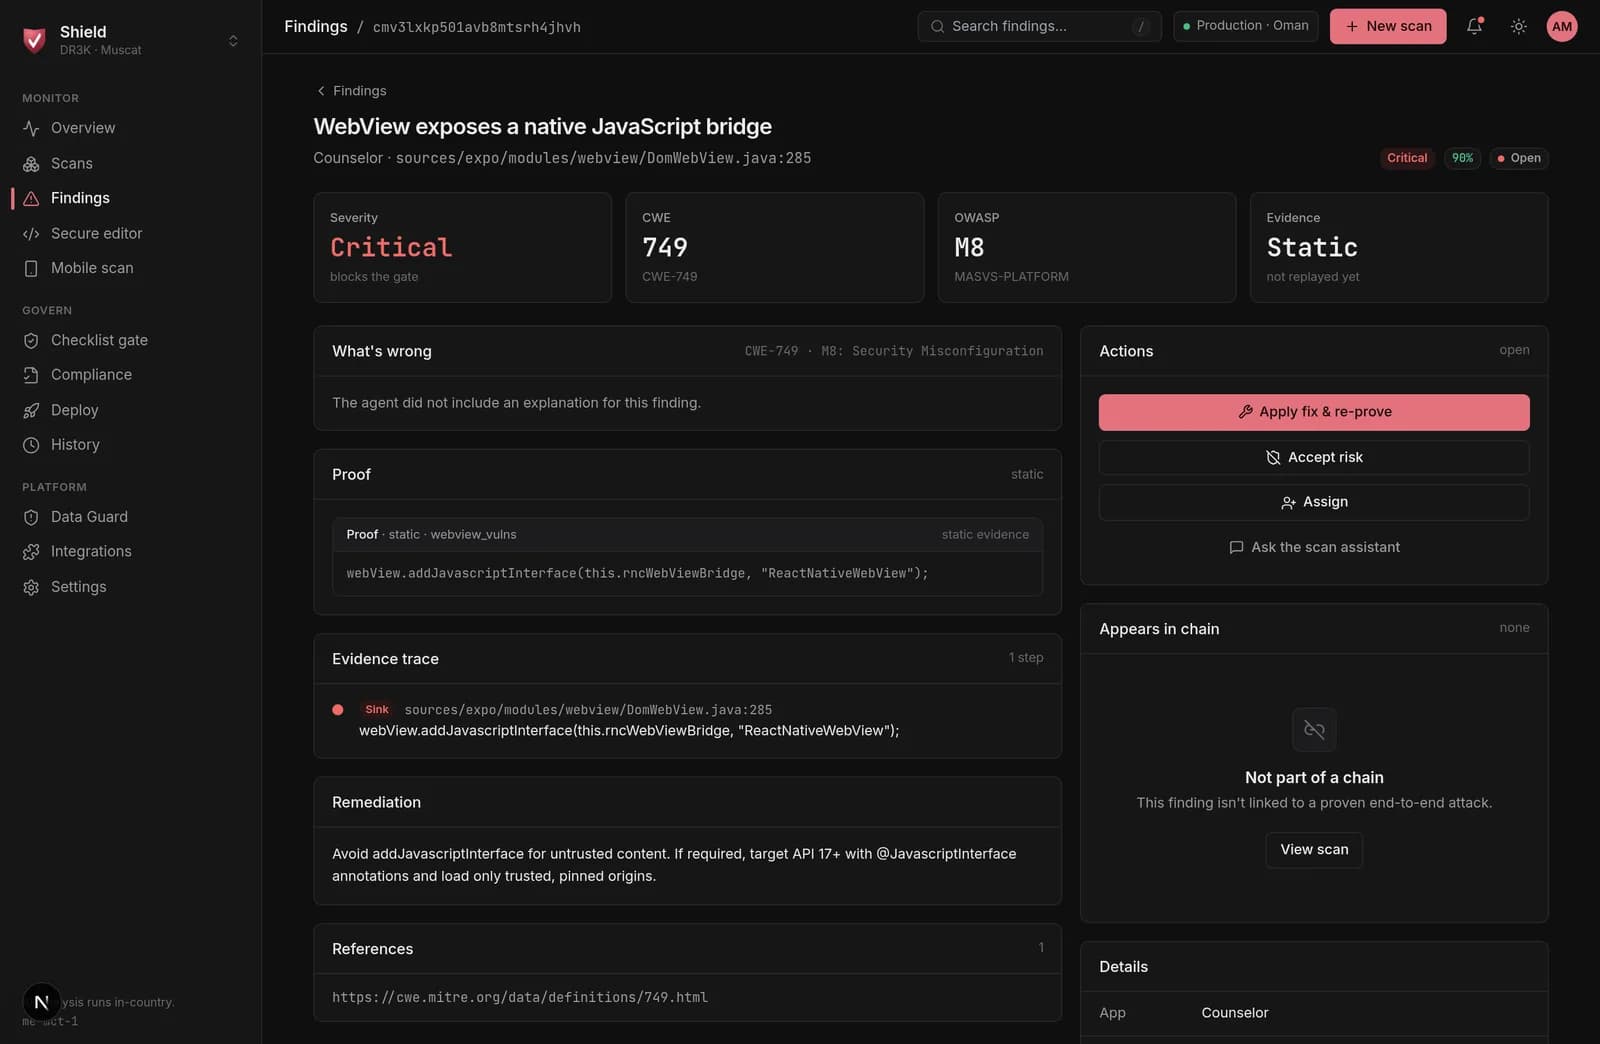
The Validator reproduces each exploit against the running target and captures exactly what happened. Not a severity guess.
- Reproduced · run against the live target, not inferred
- Captured · request, response, and the state it reached
- Gated · unproven findings never enter a report
Run the pipeline on your own code.
We stand up Shield inside your environment and show you the first proven findings.